What is Bot Client (Detuks Client) really doing?
Bot Client is owned and operated by Detuks. However, following the shutdown of Storm Client, Storm's former owner Burak resurfaced on Bot Client (Detuks Client) under the fresh account Romandinho10 (Roman - G Plugins), where Detuks gave him the "Premium Developers" role to distribute plugins.
Both Detuks and incoming DreamBot developer Aeglen have openly admitted in Discord that Allure compromised user accounts. Furthermore, users inspecting Detuks's client logs found it running the exact same OpenOSRS codebase that Storm used, while Roman magically dropped a complex ToA script within days of joining.
Accounts Are Still Being Hijacked
Victims are reporting hijacked RuneScape accounts tied to Bot Client's cloud hosting. Detuks confirms a "quite serious" breach of cloud credentials entered on the website — then blames an employee of a "100b+ company" hosting provider. Members, rival client owners, and the wider community aren't buying it.
~30 users
Cloud accounts accessed, per Detuks
UK logins
Jagex flagging suspicious logins on victims
Plain text
Members allege logins stored without encryption
SEP 18, 2026 — THE HIJACKS SURFACE
Victim Gets Jagex "Suspicious Login" Alert From the UK
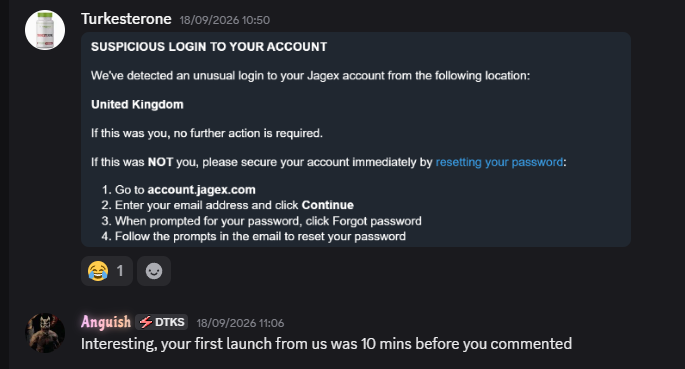
Takeaway: A victim posts an official Jagex hijack warning — and the first response from Bot Client staff is to blame the victim's timing instead of investigating.
1:20 AM — DETUKS CONFIRMS THE BREACH
"This Is Quite Serious Issue" — Cloud Credentials Accessed
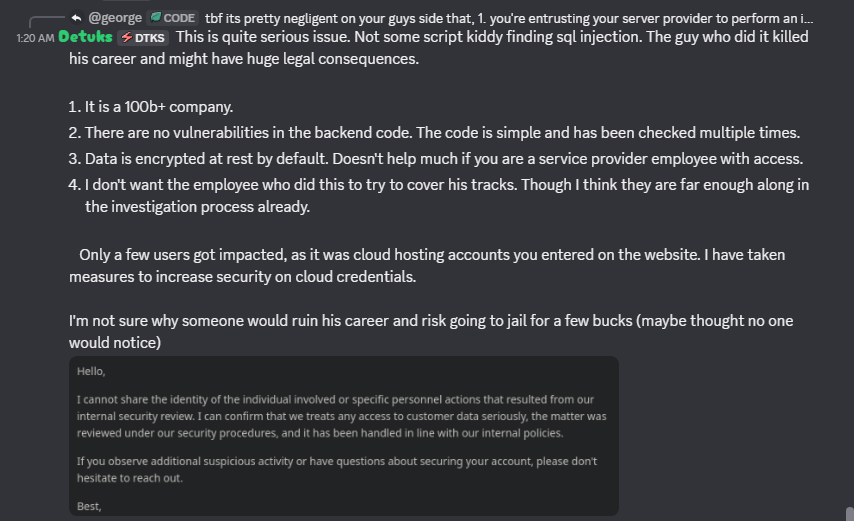
Takeaway: Detuks admits cloud hosting credentials entered on the website were accessed — while pre-emptively insisting his own code has "no vulnerabilities" and pinning everything on a hosting provider employee.
THE OFFICIAL THEORY — ~30 USERS, "KEEP IT PRIVATE"
Detuks Blames a Rogue Employee at a "Big Big Company"
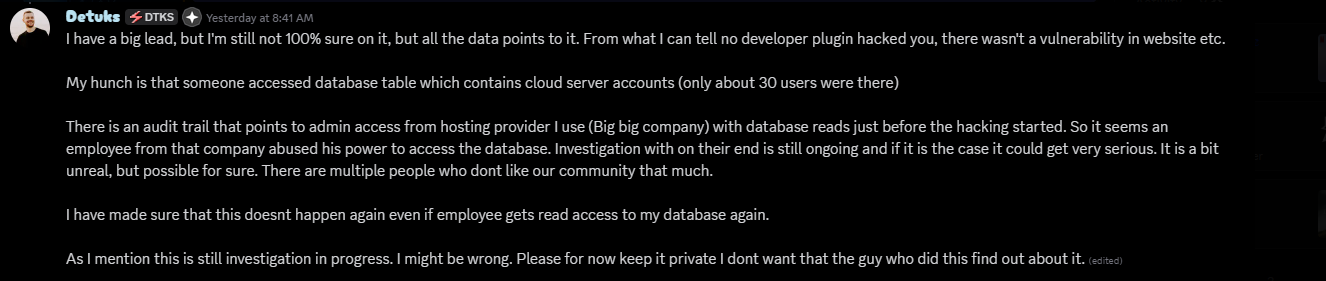
Takeaway: The official story asks you to believe a rogue employee at one of the world's largest companies risked their career — and asked victims to keep it quiet in the meantime.
THE COMMUNITY ISN'T BUYING IT
Two Theories — and Only One Sounds Believable
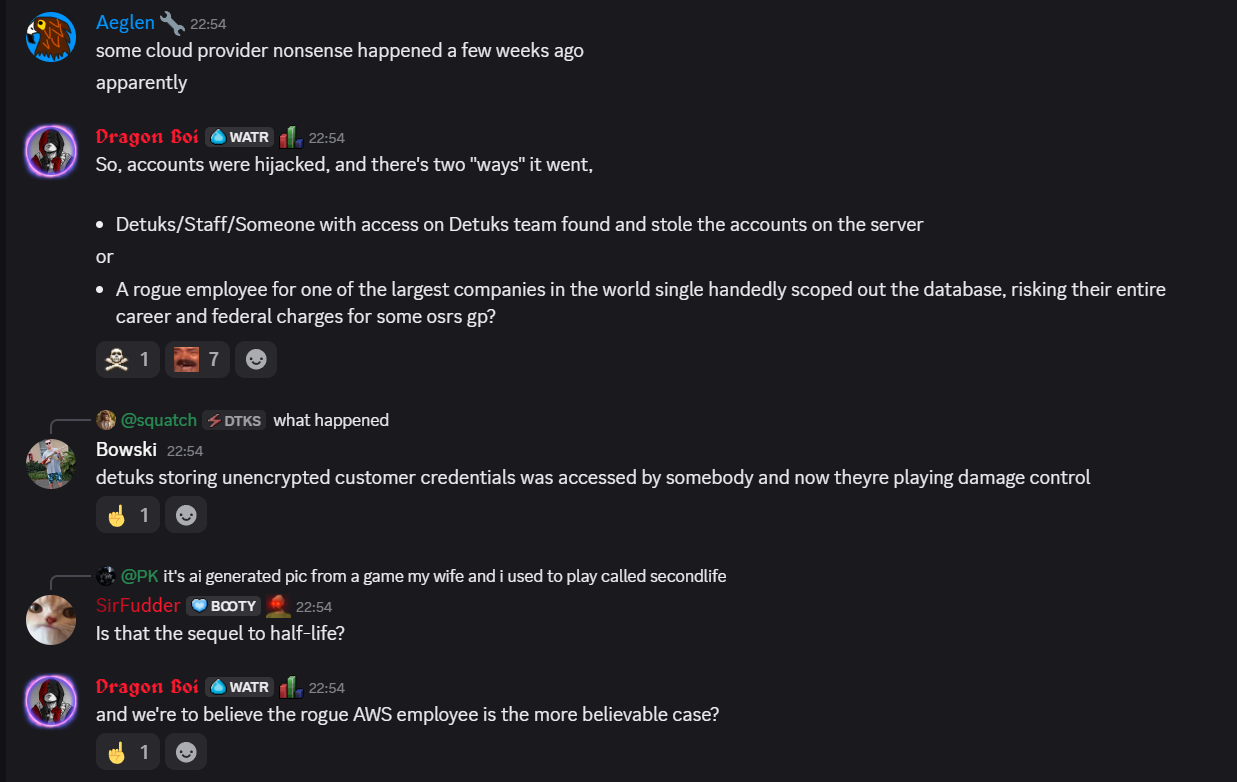
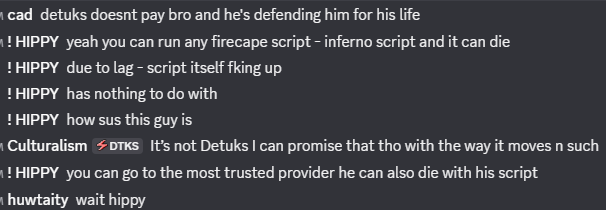
Takeaway: Even Detuks's defenders can only offer promises — while critics point at the unencrypted credential store sitting on Detuks's own server.
MEMBERS ALLEGE PLAINTEXT STORAGE
Members Say Logins Were Stored Without Encryption
🤡🤡 storing user accounts w/o encryption is just lazy 😂😂 assume it's from his "bot hosting" on bot client
They have a sketchy past doing sketchy things idk what more ppl want to validate, you think someone making multiple hundreds / thousands daily is stealing gold?
Screenshots pending — quoted verbatim from Discord
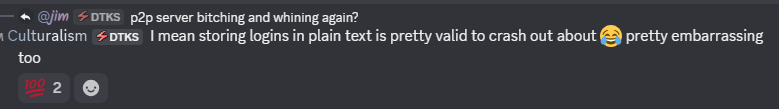
If you're storing something that can be used to log in to an account, it should be encrypted. 0 reason for it to not be.
Screenshot pending — quoted verbatim from Discord
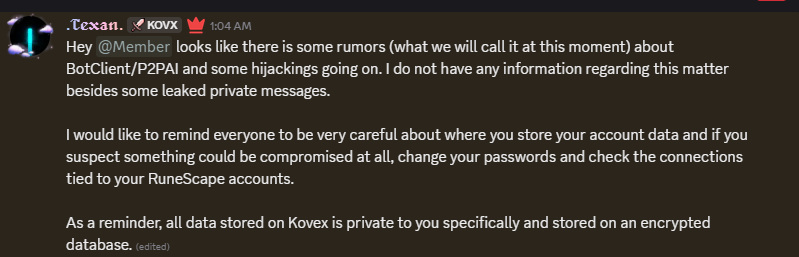
Takeaway: Detuks claims "encrypted at rest" — while members allege logins were stored in plain text. A rival client owner publicly warns users while advertising that Kovex encrypts everything.
DAMAGE CONTROL
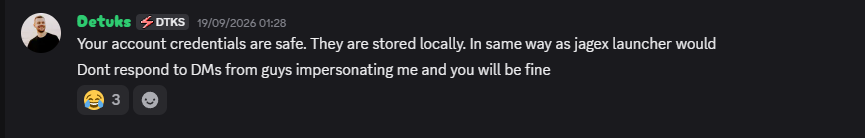
"Your Credentials Are Safe" — Trust Us
some cloud provider nonsense happened a few weeks ago apparently
Screenshot pending — quoted verbatim from Discord
Takeaway: After the breach of cloud credentials, the official line is "stored locally, just like the Jagex launcher" — directly contradicting the admission that website-entered cloud accounts were accessed.
Detuks Says vs. What Members Say
Detuks says
- "There are no vulnerabilities in the backend code"
- "Data is encrypted at rest by default"
- "Your account credentials are safe. They are stored locally"
- Only "a few users" impacted — a rogue hosting employee did it
Community members say
- "storing logins in plain text is pretty valid to crash out about 😂 pretty embarrassing too" — Culturalism (community member)
- "storing user accounts w/o encryption is just lazy" — Culturalism (community member)
- "detuks storing unencrypted customer credentials was accessed" — community report
- "It should be encrypted. 0 reason for it to not be." — Nezz
1. If you ever entered cloud hosting credentials on the Bot Client website, rotate every one of them immediately — Detuks confirms that database table was accessed.
2. Check your Jagex account for unrecognized logins and secure it via account.jagex.com (Forgot password flow) if anything looks off.
3. Enable the Jagex Authenticator on every account and never reuse those passwords anywhere else.
4. Do not store RuneScape logins in any third-party client or website that cannot show you encrypted storage.
Clarifying the Roles: Detuks, Burak, and Allure
A breakdown of who owns the platform, who wrote the plugins, and who is currently active.
Detuks is the sole owner and operator of the Bot Client platform.
Detuks accepted former Storm Client developers onto his platform and assigned Burak the Premium Developers role.
Burak was the owner of storm-client.com. After Storm shut down, he created the fresh account Romandinho10 (Roman - G Plugins).
He possessed Storm's plugin source code and re-released it on Detuks's client under the "G Plugins" brand.
Allure and Burak are two different people.
Allure developed the original Allure plugin suite for Storm Client. Burak, as Storm's owner, had the source code and is now republishing it.
Detuks & Aeglen Openly Admit Allure Compromised Accounts
Discord statements from Detuks (Bot Client owner) and Aeglen (DreamBot developer migrating to the platform) acknowledging Allure's credential theft history. Click any image to pop out and view full-size.
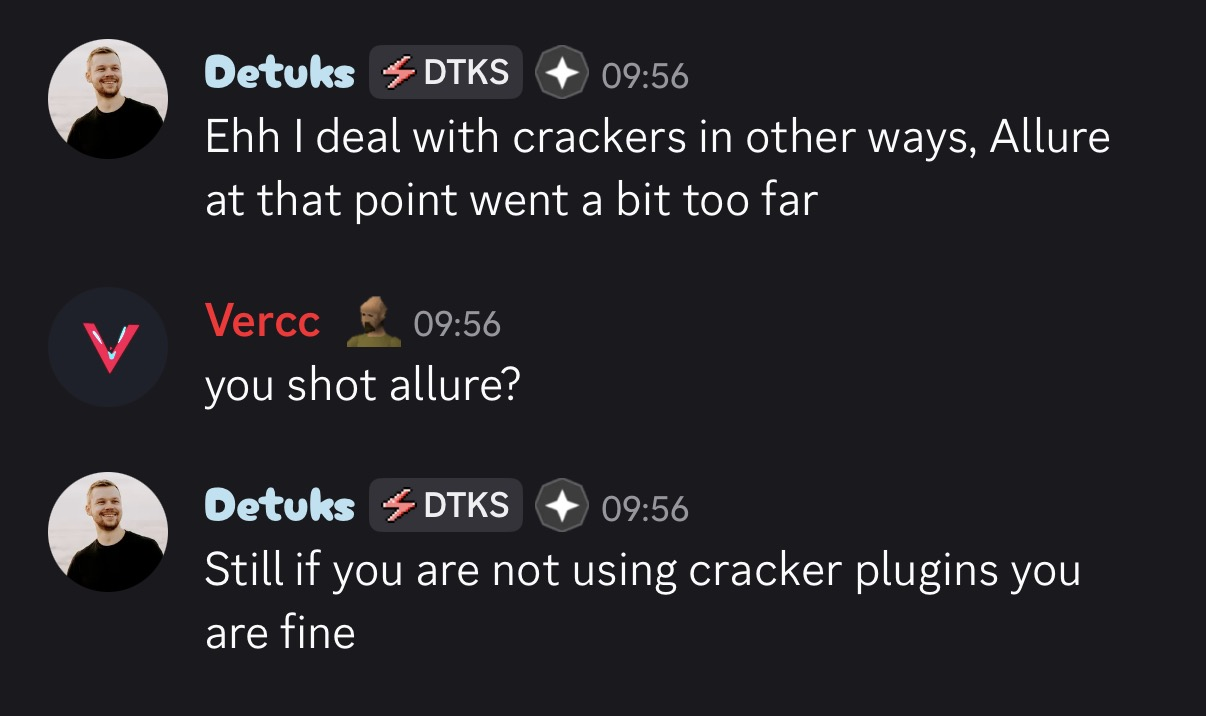
Takeaway: Detuks does not dispute credential theft occurred. He openly acknowledges Allure "went a bit too far" and attempts to normalize it by claiming regular users are "fine".
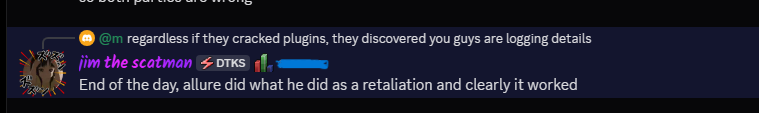
Takeaway: A Bot Client team member (jim the scatman, DTKS role) does not deny the logging — he openly confirms "you guys are logging details" and justifies Allure's credential theft as "retaliation" that "clearly it worked".
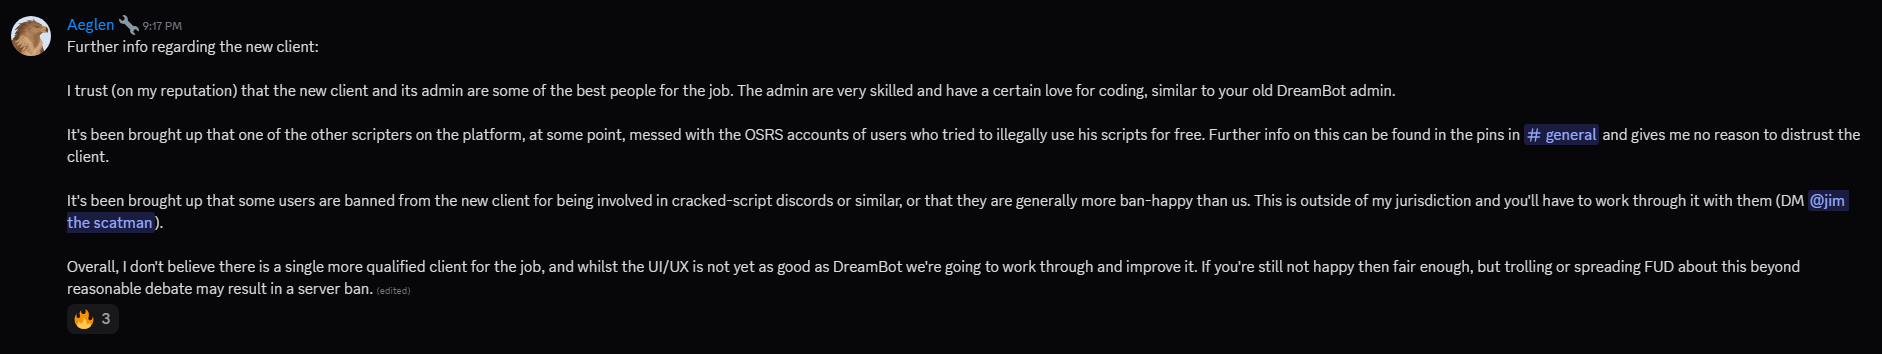
Takeaway: Aeglen explicitly confirms to his userbase that a scripter on Detuks's platform previously messed with the OSRS accounts of users.
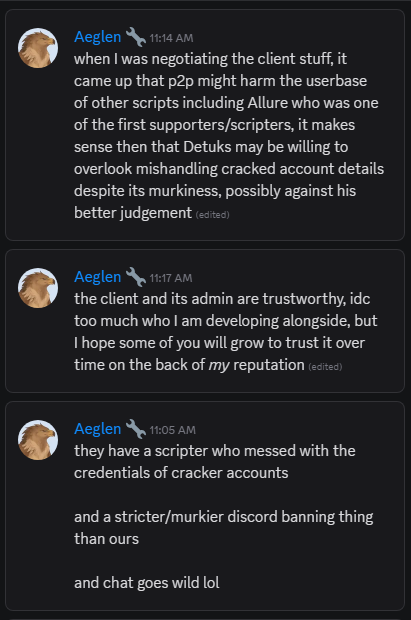
Takeaway: Aeglen confirms that during client negotiations, Detuks was willing to "overlook mishandling cracked account details" because Allure was an early supporter.
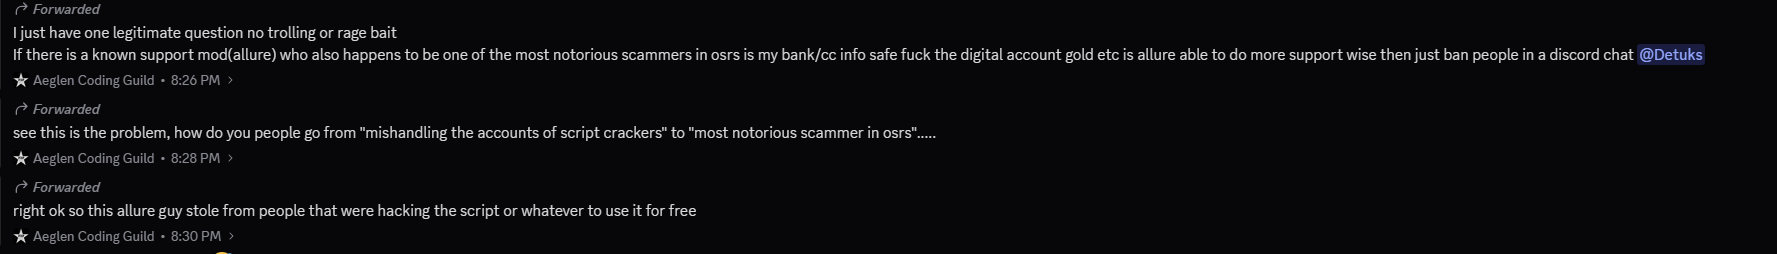
Takeaway: Even within Aeglen's own community, users openly describe Allure as "one of the most notorious scammers in OSRS" who "stole from people" — and question why Detuks would associate with him.
Burak's Fresh "Romandinho10" Account & Plugin Line
Evidence documenting Burak joining Bot Client (Detuks Client) under a fresh account and re-releasing Storm Client's plugins.
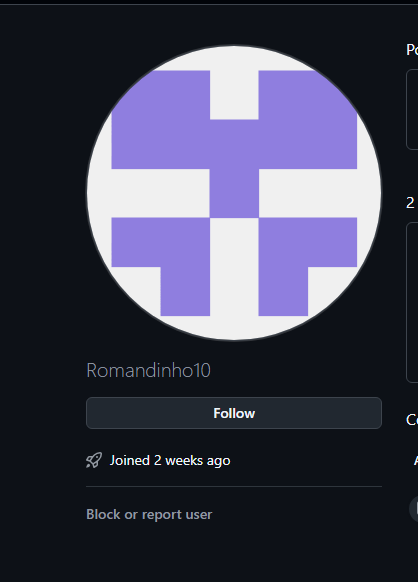
Burak operating under the fresh handle Romandinho10 on Bot Client (Detuks Client).
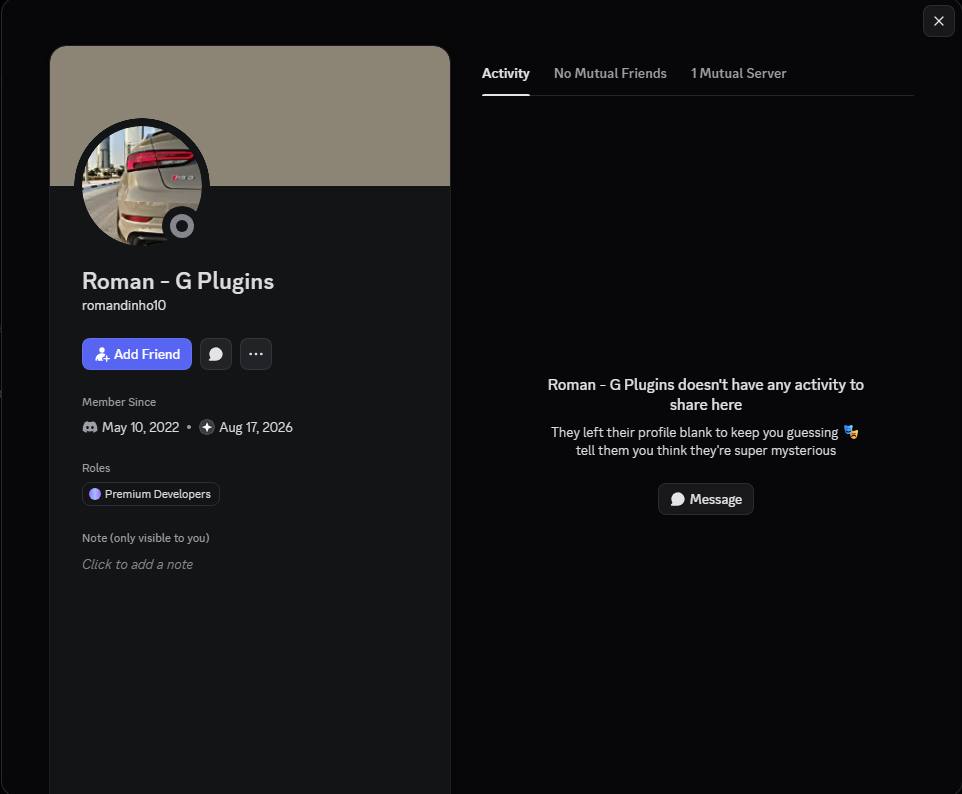
Detuks assigned Burak the Premium Developers role upon joining.
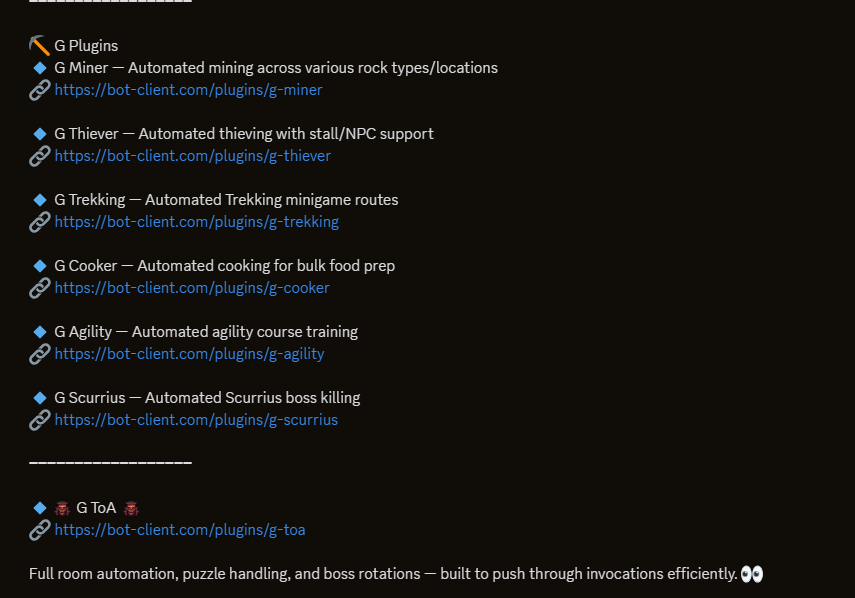
As Storm's owner, Burak held the uncompiled plugin source code and immediately republished the catalog under the "G Plugins" label on Detuks's client.
The "G Plugins" Line: Recycled Storm Client Codebase
Upon receiving the Premium Developers role from Detuks, Burak began releasing plugins under the "G Plugins" label. Because Burak was the owner of Storm Client, he possessed the uncompiled source code for all of Storm's plugins and has simply repackaged them for Bot Client (Detuks Client):
• G ToA (Tombs of Amascut raid automation)
• G Scurrius (Scurrius boss automation)
• G Miner (Mining automation)
• G Thiever (Thieving & pickpocketing)
• G Trekking (Temple Trekking minigame)
• G Cooker (Bulk food cooking)
• G Agility (Rooftop agility courses)
The ToA Give-Away
Months of complex raid automation appearing just days after "Roman" joined the platform.
All of the former Storm developers moved over to Detuks's client. When "Roman" created his account 2 weeks ago, he immediately released a complex Tombs of Amascut (ToA) automation plugin.
ToA plugins require extensive room mechanics, puzzle automation, gear switching, and invocation routines. Nobody writes a flawless ToA bot from scratch in a few days — it is 100% Burak recycling his Storm Client ToA codebase.
1.2GB RAM Overhead & User Pushback
DreamBot users migrating with Aeglen are openly refusing to move to Detuks's platform — even team members admit the client is bloated.
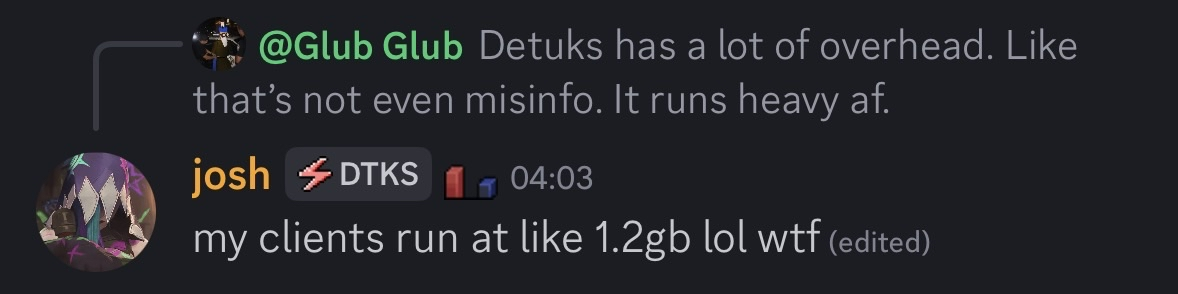
A Bot Client team member confirms client instances consume upwards of 1.2 GB of RAM each due to unoptimized overhead.
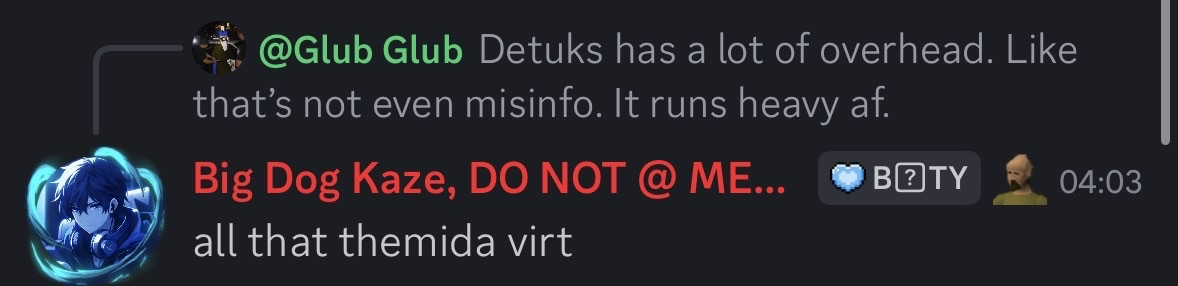
The client's Themida anti-tamper virtualization is cited as a major source of the performance overhead.
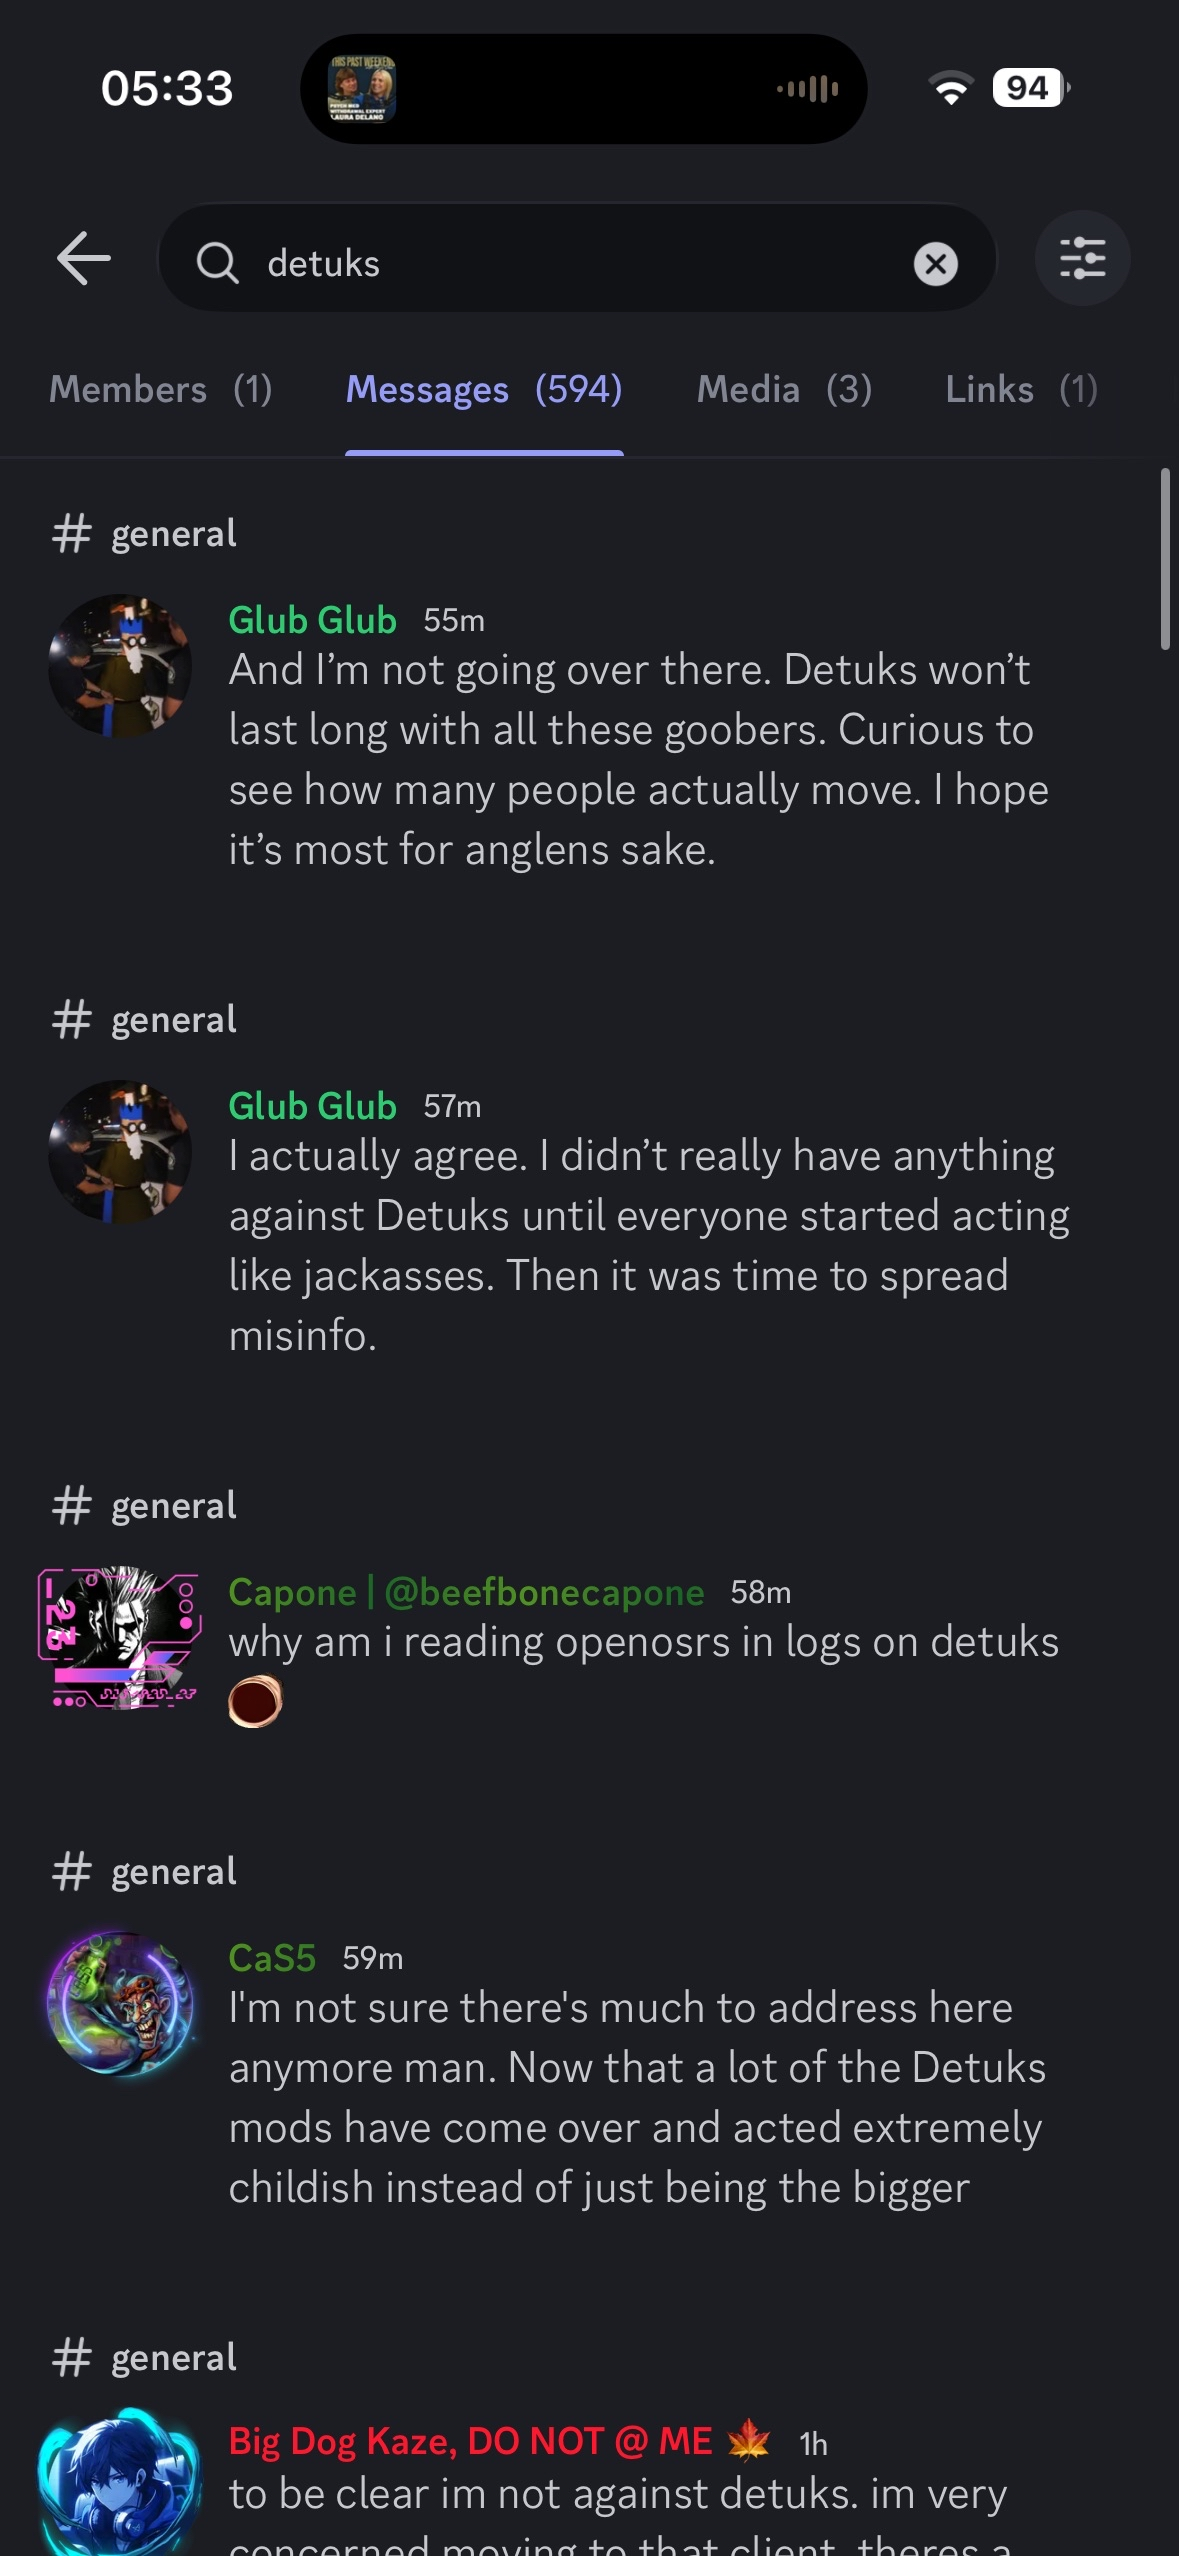
Longtime users are openly refusing to migrate, citing childish moderator behavior and concerns about the client's origins.
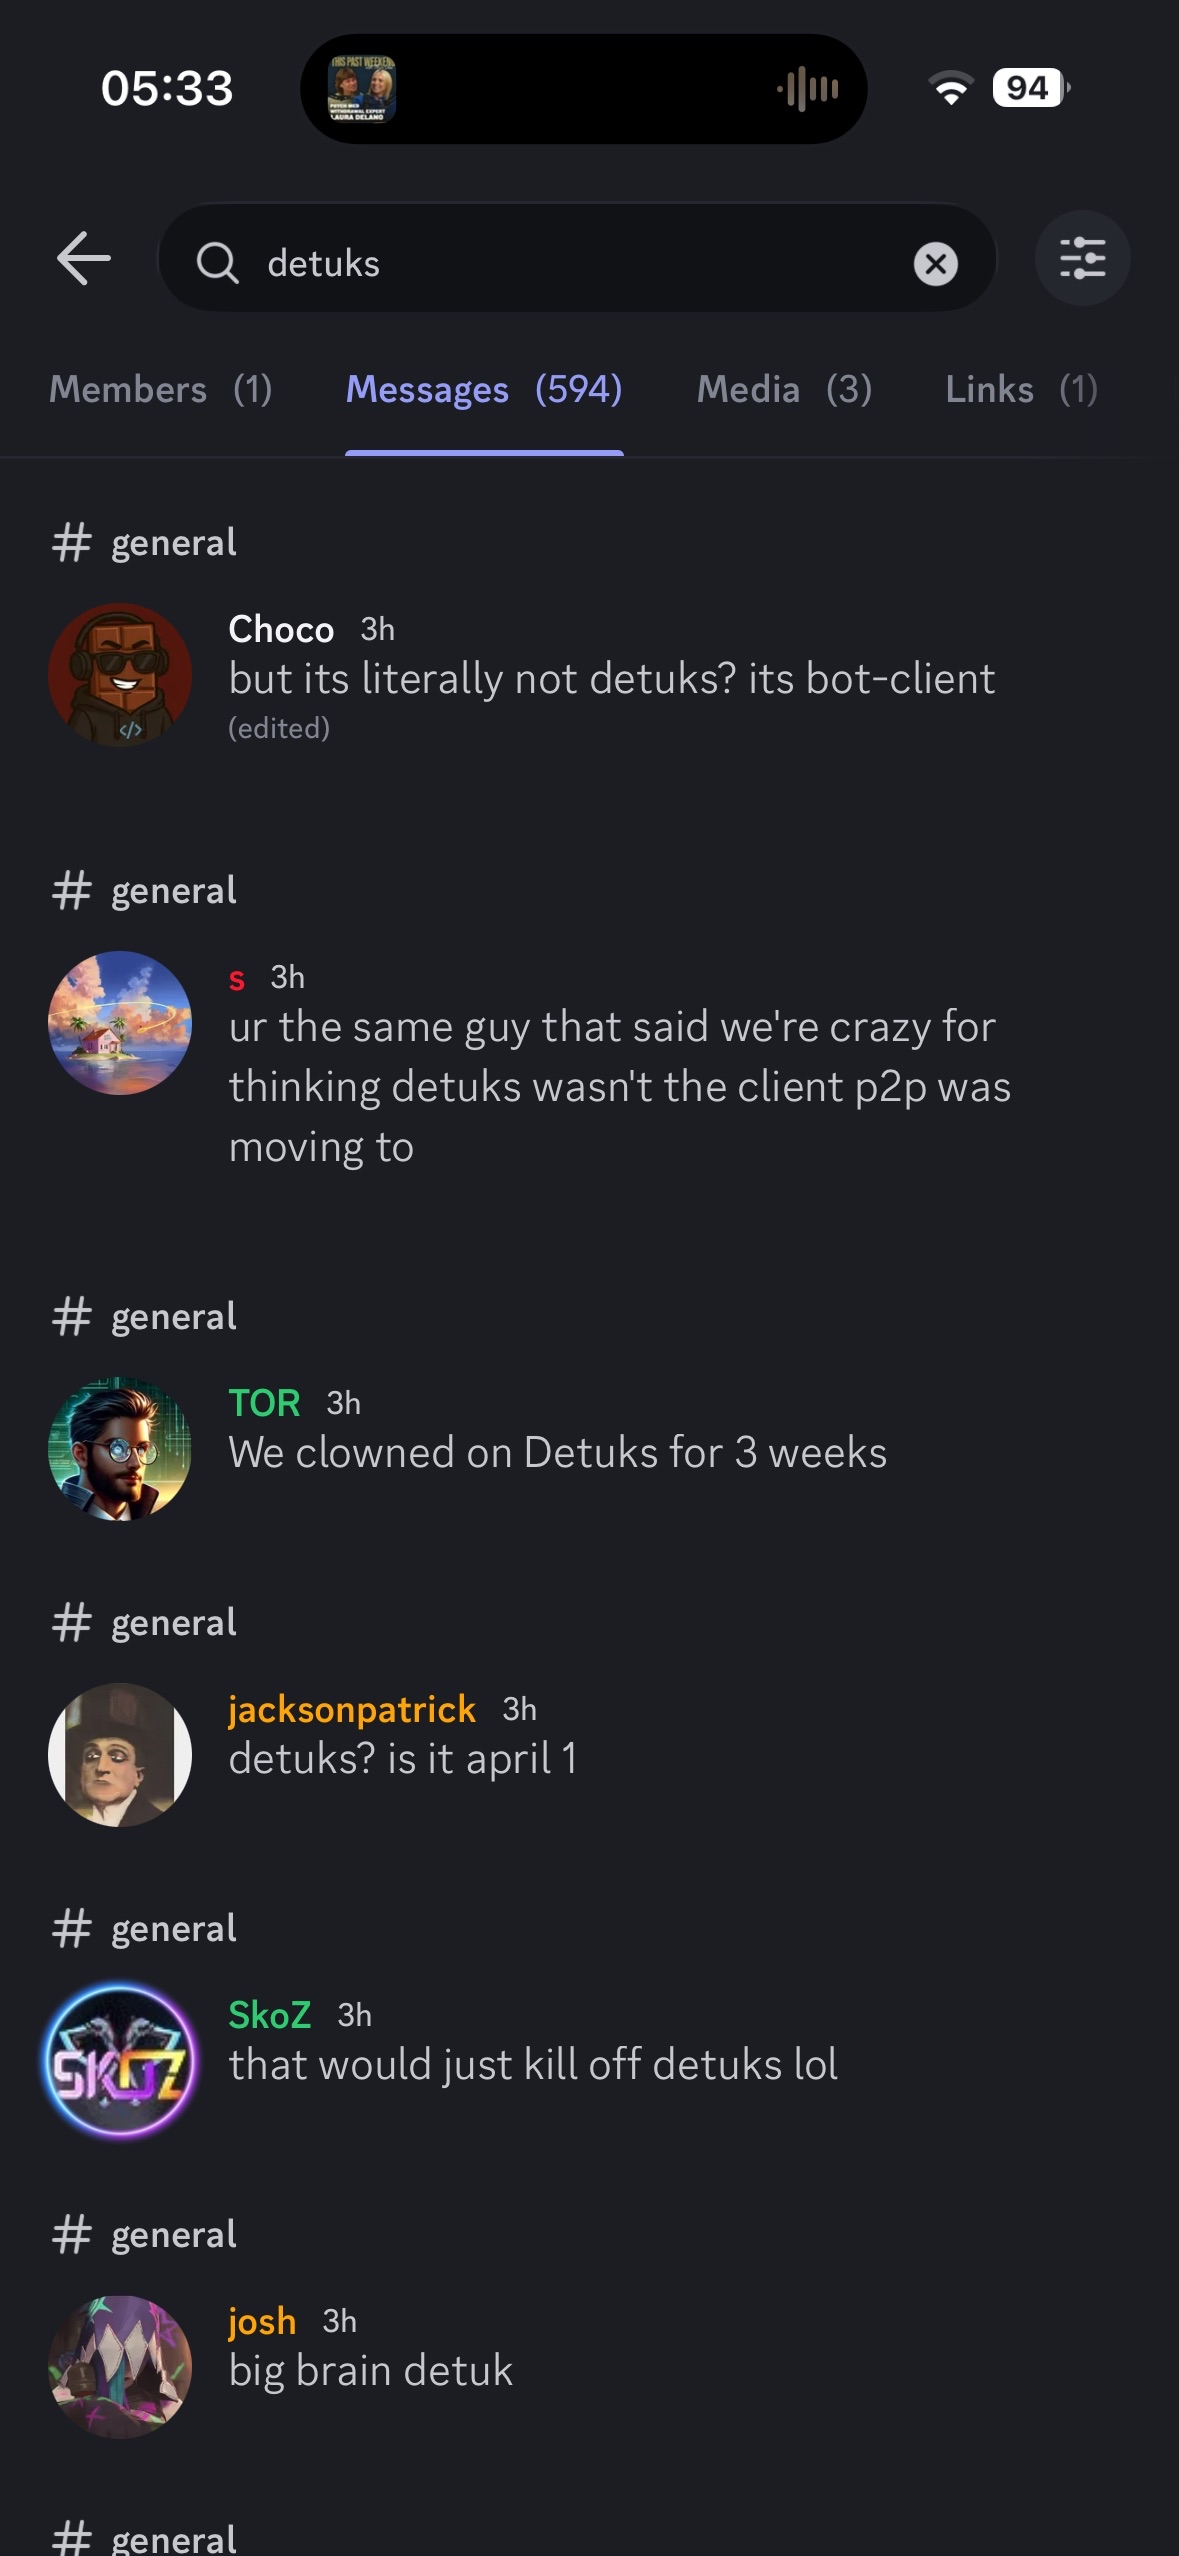
The community's reaction to the migration announcement was overwhelmingly skeptical and mocking, with users questioning the rebrand from Detuks to "Bot Client".
Technical Analysis: Inside the Allure Wildy Slayer Plugin
We decompiled the protected, obfuscated plugin JAR distributed for the Detuks/Bot Client platform and audited every outbound call it makes. Below are the exact findings — with the decompiled code, class names, and recovered strings to back each one up.
The "Allure" Plugins Are Written in Detuks's Own Namespace
The obfuscated core of this Allure-branded plugin ships under the com/detuks/ package — Detuks's own namespace. This is not a third-party plugin hosted on Detuks's platform: Detuks writes the "Allure" plugins himself. The readable classes (AllureWildySlayer, GameStateDump, the WebSocket message stack) sit alongside the obfuscated engine in o/a.class (58.5 KB).
package tree — as shipped in the JAR
com/detuks/e/a/          <- obfuscated core
com/detuks/e/a/o/a.class <- engine (58.5 KB)
com/detuks/e/a/h/a.java  <- RSA/AES-GCM crypto
com/detuks/e/a/H.java    <- hardcoded AES key

com/detuks/.../AllureWildySlayer.class
com/detuks/.../GameStateDump.class
com/detuks/.../WebSocketMessage.class
com/detuks/.../MuleStatusMessage.class5-Minute Heartbeat to api/session/check
For the entire session the plugin calls api/session/check every 5 minutes (class u/a/b). Each check-in carries the session ID, the machine's HWID fingerprint, and live plugin/player state — so the Detuks backend knows who is running, on which machine, and what they are doing at all times.
u/a/b — decompiled (simplified)
@Schedule(period = 5, unit = MINUTES, async = true)
void heartbeat() {
    POST  BASE_URL + "api/session/check"
          session : <session id>
          hwid    : <machine fingerprint>
          state   : <plugin / player state>
}HWID Fingerprinting — What It Captures About Your Machine
The plugin assembles a fingerprint from the identity signals of your computer: your operating system name and architecture, your Windows username, the computer's name on the network, your network adapter's MAC address, and your disk/volume identifiers. These are concatenated and hashed into a single stable ID that survives OS reinstalls of the plugin, password changes, and new RuneScape accounts.
That ID rides along with every 5-minute check-in. It means the operator doesn't just know an account is botting — they know which physical machine is doing it. A HWID ban follows your computer, not your account.
hwid assembly — decompiled (simplified)
String raw =
    osName          // e.g. "Windows 10"
  + osArch          // e.g. "amd64"
  + user.name       // your Windows username
  + COMPUTERNAME    // machine name on the network
  + macAddress      // network adapter MAC
  + volumeSerial;   // disk / volume identifier

String hwid = sha256(raw);  // stable machine ID
payload.put("hwid", hwid);
// attached to every api/session/check callDiscord Webhooks — Everything It Sends, and Where
Beyond the 5-minute heartbeat, the plugin reports out to two destinations: Discord webhooks carrying your RuneScape display name and public IP address, and the Detuks backend receiving session telemetry plus event reports — ban reports, quest completions, and bug reports — with room metadata streamed over its WebSocket channel.
Seven hardcoded webhook endpoints were recovered from the JAR in full — no decoding required once the string table was restored. They are reproduced verbatim on the right. Anyone can report these endpoints to Discord for revocation, which is exactly why they are published here.
recovered webhook URLs — verbatim from the JAR
POST discord.com/api/webhooks/1153807665571565639/R1FLdA7O7ITGDfmDzsKfytTGEM3ScbUs7nzBPQFkqZi8BISZIiv9SF0vqeyWDtIXj1od

POST discord.com/api/webhooks/1153808285527461958/KdTqaMoCgCPq_8vyM3x8fZ2AoS8LtIkv5w6uXsW9SSc7NL5fm_orRyUvA3U5ZBDrNeLk

POST discord.com/api/webhooks/1198772940993470464/CnXafDh3vmNexl3OuuK9WYU9-_vvwOzF-SJ9MiajEQ5oEpIcD-cZXODZvIbpoeRKmpxf

POST discord.com/api/webhooks/1456488921117491424/FiyHQBWqqw1rTsp_X4IcxfWTeSs1VIBmxj5pOOqvYOgUYvkh9zh9X6dszwKIK7lDV4S1

POST discord.com/api/webhooks/1524177021758996742/QhYho1fnjFFR0ty1p1Wc7udTGasxfM5kwN1S-2SEvm3LftLuqh7OfKYSc-BnFoNQjkPp

POST discord.com/api/webhooks/1526339256845467762/tNcRXWx8qhY70DXuOM_36HCRCIS3bdvK-EYn7cDbZOjA9ccRLEiB3drUxCE6Iuk3OZdU

POST discord.com/api/webhooks/1526341180651212870/ZZbTicxN_zYmCVj_muXTVIVcLSa-0I8wrDzdGCHK4Qew52bOgHCDaZwOuNx4ci-kU7rq

// payload: "<rs_name> | ip: <public ip>"
// plus ban / quest / bug event reportsThe Plugin Still Writes to a ".storm2" Folder
Session debug logs (session_start / session_end JSONL) are written to %user.home%\.storm2\debug\ on your machine (class i/c, local-only, never transmitted). A Storm-branded folder inside a Bot Client plugin is definitive proof of code lineage: this is Storm Client source code, lightly rebranded, running on Detuks's platform.
i/c — local JSONL logger (decompiled)
Path dir = Paths.get(
    System.getProperty("user.home"),
    ".storm2", "debug");      // <- Storm-branded

// writes:
// {"event":"session_start", ...}
// {"event":"session_end",   ...}
// local only — never transmittedThe Actual Keys — Hardcoded AES, RSA Handshake, XOR Strings
H.java carries a hardcoded AES key — f4+Etk7Rseg"q}~?L.2nM; — used with plain Cipher.getInstance("AES") (ECB) and Base64 wrapping to encrypt/decrypt messages. Since the key ships inside the JAR, this "encryption" is purely cosmetic: anyone can decrypt exactly what the backend can.
h/a.java implements proper hybrid encryption: a random AES-256-GCM session key encrypts the payload, then RSA/ECB/OAEPWithSHA-1AndMGF1Padding wraps that session key with an embedded X509 public key — only the operator's private key reverses this. There is also j/b.java (AES/CBC config-blob decryption, key = SHA-256(password + salt)) and a leftover dev-test sender in ai.java (AES/CFB over UDP to 192.168.1.100:12345 with the placeholder key your-32-byte-key). The XOR layer scrambles every string in the JAR — endpoints, URLs, wire formats — so none of it appears in plaintext until runtime.
recovered key material — verbatim from the sources
// H.java — hardcoded AES key (verbatim)
new SecretKeySpec(
  "f4+Etk7Rseg\"q}~?L.2nM;".getBytes(), "AES")
Cipher.getInstance("AES")  // = AES/ECB, Base64-wrapped

// h/a.java — hybrid RSA + AES-256-GCM
sessionKey = KeyGenerator("AES").init(256)
payload    = AES/GCM/NoPadding(sessionKey, iv[12])
wrapped    = RSA/ECB/OAEPWithSHA-1AndMGF1Padding(
               embeddedX509PublicKey, sessionKey)
// only the operator's private key reverses this

// j/b.java — config blobs
key = SHA-256(password + salt)  // AES/CBC/PKCS5

// ai.java — leftover dev/test sender
UDP 192.168.1.100:12345
key = "your-32-byte-key"| String | Location | What it is |
|---|---|---|
| api/session/check | u/a/b | The 5-minute heartbeat endpoint |
| session_start / session_end | i/c | Local-only JSONL debug log → %user.home%\.storm2\debug\, never sent |
| |session: | a/q | Seeded RNG log label (session|decision), local |
| OAUTH2 → JL auto-login | a/h | Login screen index handling — presses Enter only, no token captured |
| SecretKeySpec / SecretKey | H, ai, j/b, h/a | AES/XOR + RSA embedded keys — string/API obfuscation, not credentials |
| runtime-action-token | evidence JSON | The analysis kit's own redaction label for a config toggle — not plugin code |
To keep this investigation honest: unlike the original Storm Client Allure plugins — which captured usernames, passwords, session tokens, and Discord identities — this specific build contains no plaintext password theft and no session token capture. Every candidate was swept and accounted for:
JX()— an obfuscated RuneLite API stub method, not a token (it is the widgetfontIdgetter:f2.JX(), called atGameStateDump.java:107)jx_/jX_— obfuscated method names inside the API ABI-stubs JAR (net/runelite/a/f/h.class)JxPm7/jX— coincidental characters inside XOR-encoded string blobs; the decoded constants are the knownMULE_STATUS/TRADE_REQUEST/ login-log stringsOAUTH2 → JL auto-login(classa/h) — login-screen index handling that presses Enter only; no token is ever capturedruntime-action-token— the analysis kit's own redaction label for a config toggle, not plugin code
What it does contain is constant heartbeat telemetry, HWID fingerprinting, Discord webhooks carrying your RS name and public IP, real-time mule/trade WebSocket coordination, and a .storm2 debug folder that betrays its Storm Client origins.
The absence of credential theft in one plugin does not clear the platform: the owners themselves admitted on record what Allure did previously, and the same team operates this codebase. Treat every binary from this platform as untrusted.
1. Detuks and Aeglen have both confirmed that scripters on this platform previously compromised user credentials.
2. Do not input your primary RuneScape credentials or session tokens into Bot Client (Detuks Client) software.
3. If you have already authenticated or used Bot Client (Detuks Client) tools, change your password and reset your Jagex session tokens.
4. Enable 2FA (Jagex Authenticator) and stick to verified open-source clients like official RuneLite.
Curious about TwiLite?
Check out our report on twilite.lol →
More Evidence & Analysis Coming Soon
Additional reverse-engineering analysis, packet captures, and source diffs will be published here as the investigation progresses.